Enterprise Cloud SIEM Platform.
Complete Data Ownership. Save Up To 70% in TCO.
Comprehensive cloud security telemetry correlation, investigation, and visualization designed for banking institutions, GLCs, and enterprises in Malaysia. Operating 100% within your private environment with zero third-party data sharing.
Malaysian Cybersecurity Compliance Standards
SIEMz is purpose-built to fulfill regulatory frameworks mandated for financial institutions, government agencies, and National Critical Information Infrastructure (NCII) operators.
BNM RMiT
Risk Management in Technology
Fulfills rigorous technology governance, cyber risk management, and log integrity audit requirements for banking, capital markets, and insurance sectors across Malaysia:
- ✓ Immutable Audit Trail: All system activities, privileged access attempts, and security events are logged with write-once retention preventing deletion or tampering.
- ✓ Logging Bypass Detection: Real-time automated alerting whenever audit logging mechanisms are disabled, disrupted, or maliciously terminated.
- ✓ Private Zone Network Segmentation: Deployed into isolated private subnets ensuring zero exposure for transaction data and core banking systems.
- ✓ Tiered Log Retention Lifecycle: Seamless tiered storage lifecycle (hot/warm operational indices and cold archival storage) retaining logs up to 7 years to satisfy regulatory retention mandates.
Cyber Security Act 2024
Cyber Security Act 2024 (Act 854)
Tailored for National Critical Information Infrastructure (NCII) entities across 11 key designated sectors (Energy, Banking, Transportation, Government, Healthcare, etc.):
- ✓ Mandatory Telemetry Monitoring: Continuous ingestion and automated analysis of security telemetry across the entity's entire operational digital estate.
- ✓ Rapid Incident Notification: Automated anomaly and breach detection engineered to meet statutory incident reporting timelines to CyberSecurity Malaysia / NC4 within prescribed SLAs.
- ✓ 100% Domestic Data Sovereignty: Threat telemetry and cyber defense operational intelligence remain exclusively in Malaysian territory with zero exposure to foreign jurisdictions.
- ✓ Certified Auditor-Ready Reporting: Executive compliance dashboards and audit reports prepared for annual audits by licensed cybersecurity assessment practitioners.
PDPA Compliance
Personal Data Protection Act (Act 709)
Safeguards customer personal data, employee records, and confidential corporate information against unauthorized disclosure or breach:
- ✓ Technical Security Safeguards: Defends sensitive data against unauthorized exfiltration using industry-standard TLS 1.3 in-transit and AES-256 at-rest encryption.
- ✓ Customer-Owned KMS Encryption: Cryptographic keys are exclusively owned and managed 100% by your organization with zero third-party visibility.
- ✓ Zero Cross-Border Transfer: Eliminates cross-border data transfer risks as all telemetry processing and storage remain strictly within Malaysia.
- ✓ Role-Based Access Control (RBAC) & Masking: Strict Least Privilege access controls with native support for pseudonymization and PII masking.
SIEM Framework: People, Process & Technology
Successful cybersecurity operations require more than software alone—it demands the balanced synergy of advanced technology, standardized response playbooks, and certified local talent.
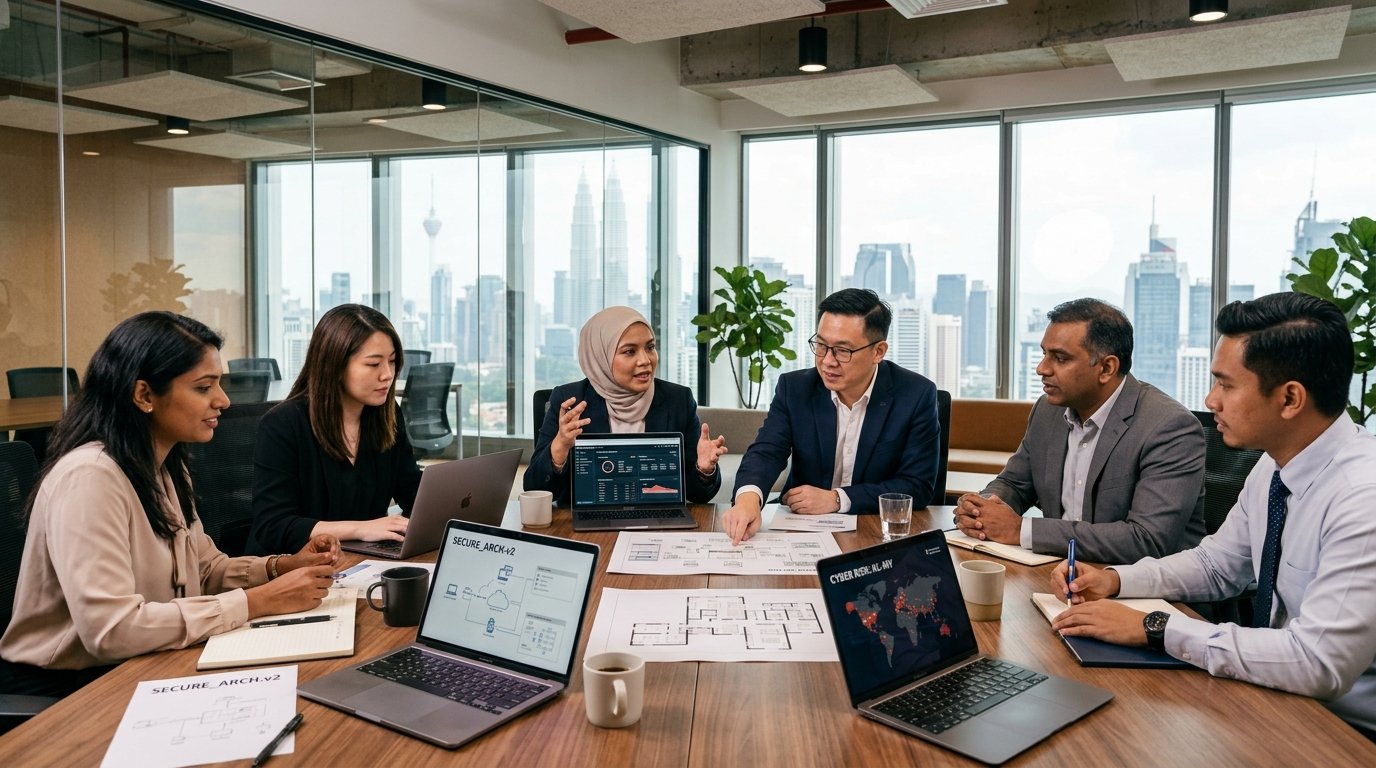
Collaborative Defense Alongside Your Security Team
Our local Malaysian cybersecurity experts partner with your organization from initial architecture design and detection engineering through to ongoing 24/7 SOC operational support.
Technology
High-Performance Open Core & Data Sovereignty
Scalable, resilient private cloud infrastructure free from ingestion penalties:
- ✓ High-Performance Open Query Engine: Open-core search engine processing millions of events per second (EPS) with rapid query latency.
- ✓ Automated ECS Normalization: In-flight Elastic Common Schema taxonomy transformation across all incoming telemetry streams.
- ✓ Customer-Managed KMS Encryption: AES-256 and TLS 1.3 encryption inside private VPC subnets with zero public internet exposure.
- ✓ Threat Intel (IoC) & GeoIP Enrichment: Real-time correlation with STIX 2.x feeds, malicious IP reputation, and MaxMind GeoIP.
Process
SOPs, Incident Playbooks & Compliance SLAs
Standard operating procedures aligning threat triage with statutory reporting mandates:
- ✓ Incident Response Playbooks: Standardized operational workflows aligned with severity tiers (P1-Critical to P4-Low).
- ✓ National Statutory SLA Reporting: Automated notification pipelines meeting Act 854 guidelines to NC4 / CSM.
- ✓ Log Lifecycle Governance: Scheduled integrity audits, bypass logging alarms, and automated archival retention up to 7 years.
- ✓ Proactive Threat Hunting: Regular hypothesis-driven search cycles uncovering advanced persistent threats before escalation.
People
SOC Analysts, Engineers & Security Advisers
Skilled cybersecurity personnel managing day-to-day defense operations:
- ✓ 24/7/365 SOC Security Analysts (Tier 1 – Tier 3): Continuous eyes-on-glass triage separating true attacks from benign noise.
- ✓ Detection & Integration Engineers: Local specialists assisting with log source onboarding, rule engineering, and dashboard customizations.
- ✓ Regulatory Compliance Advisers: Guiding architectural posture to maintain continuous compliance with BNM and national cyber standards.
- ✓ Internal Team Empowerment (Knowledge Transfer): Upskilling your internal IT and security personnel for long-term self-sufficiency.
What is the Elastic Common Schema (ECS)?
An open industry-standard schema specification that unifies disparate vendor log formats into a single, consistent security analytics taxonomy.
Before ECS Normalization (Heterogeneous Logs)
Each security appliance and application generates disparate field names. SOC teams must memorize dozens of syntax variations to investigate a single security event:
With SIEMz ECS Normalization (Unified Standard)
All telemetry streams are automatically transformed at the ingestion pipeline into a standardized, hierarchical schema:
source.ip: 10.10.1.2 investigates all assets, firewalls, and servers simultaneously in seconds.
Key ECS Field Normalization Mapping Table
How SIEMz automatically maps heterogeneous security telemetry into unified standard fields:
| Telemetry Category | Disparate Vendor Fields | Standardized ECS Field | SOC Operational Advantage |
|---|---|---|---|
| Source IP Address | src_ip, src_addr, clientip, c-ip | source.ip | Single IP query searches entire digital estate simultaneously. |
| User Identity | usr, user_name, sAMAccountName, uid | user.name | Tracks user activity across servers, cloud systems, and VPNs. |
| Destination Port | dport, dst_port, destination_port | destination.port | Identifies port scanning attempts and exfiltration patterns. |
| Security Action | act, action, status, verdict | event.action | Standardizes verdict statuses (allow, deny, block, alert). |
| Threat Indicator (IoC) | sig_name, rule_title, threat_id | threat.indicator.name | Correlates real-time STIX 2.x threat intelligence feeds. |
Universal Search Queries
Analysts no longer memorize vendor-specific syntaxes. All incident triage executes through unified standard query filters.
Cross-Vendor Correlation
Identifies full attack kill-chains from perimeter firewall probing to lateral movement across internal enterprise servers.
In-Flight Threat Intel (IoC)
IPs and domains are enriched in-stream with MaxMind GeoIP and threat intelligence feeds with zero manual ETL scripting.
Vendor-Neutral Freedom
Freely upgrade or introduce new telemetry sources without rebuilding existing dashboards or alerting rules.
Advanced Security Analytics Capabilities
Engineered for multi-account visibility, automated cross-source correlation, and rapid incident response.
Automated Schema Normalization (ECS)
Eliminates disparate data silos. Management audit logs, network flow records, DNS queries, firewall telemetry, and host system events are automatically transformed into the standard Elastic Common Schema (ECS).
In-Flight Threat Intelligence (IoC) & GeoIP
Incoming logs are enriched in real time with IP reputation indicators, STIX 2.x threat intelligence feeds, known malicious infrastructure, Tor exit nodes, and MaxMind GeoIP geolocation.
Private Network Isolation
Deployed entirely into your organization's private subnets. Protected by customer-managed KMS encryption keys with zero telemetry data shared to public multi-tenant clouds.
Open Architecture vs. Proprietary Legacy SIEM
Why Malaysian GLCs and financial institutions are transitioning to modern open architecture models.
| Evaluation Criteria | SIEMz Malaysia | Traditional Closed SaaS SIEM |
|---|---|---|
| Commercial Pricing Structure | Predictable MYR billing • Zero per-GB volume penalties | Volatile USD per-GB fees that surge with log volume growth |
| Data Sovereignty & Residency | ✓ 100% Hosted in private Malaysian environments | Stored on shared multi-tenant SaaS servers in foreign jurisdictions |
| Data Format & Schema | ✓ Open standard Elastic Common Schema (ECS) | Proprietary query syntaxes with restrictive vendor lock-in |
| Long-Term Archival Cost | Ultra-low-cost tiered cold object storage lifecycle | Expensive proprietary retention forcing artificial log truncation |
Frequently Asked Questions (FAQ)
Clear answers regarding deployment, data sovereignty, and regulatory compliance for SIEMz in Malaysia.
What is the Elastic Common Schema (ECS) and how does it streamline SOC operations?
ECS is an open industry-standard data schema specification that normalizes heterogeneous vendor log field names into a unified standard taxonomy (e.g., standardizing multiple firewall, proxy, and cloud IP fields into source.ip). This enables security analysts to query across all infrastructure components with one single universal query, accelerates cross-source correlation, and eliminates vendor lock-in.
How does SIEMz ensure compliance with the Personal Data Protection Act (PDPA)?
SIEMz guarantees 100% domestic data residency within Malaysia with zero unauthorized cross-border transfers. All telemetry is secured using robust AES-256 and TLS 1.3 encryption with customer-managed KMS keys, complemented by granular Role-Based Access Control (RBAC) and privacy-preserving PII masking.
What are the primary advantages of SIEMz over traditional proprietary SaaS SIEMs?
SIEMz delivers 100% domestic data sovereignty in your own private environment, eliminates volatile USD per-GB ingestion penalties (yielding up to 70% budget savings), automates normalization via the open Elastic Common Schema (ECS), and provides turnkey compliance with Malaysian financial and national cyber security standards.
How does SIEMz support BNM RMiT and Cyber Security Act 2024 compliance?
SIEMz incorporates immutable audit logging, automated detection of logging service tampering or bypass, strict private network segmentation, and tiered hot/warm/cold storage up to 7 years to satisfy regulatory retention mandates.
Is our organization's security telemetry and data hosted domestically in Malaysia?
Yes, 100% of all log records, search indices, and telemetry archives are stored and processed exclusively in Malaysian domestic zones under your exclusive organizational control, with zero exposure to foreign jurisdictions.
What telemetry and log sources are supported for ingestion?
SIEMz supports comprehensive integration across cloud audit trails, VPC flow logs, DNS queries, firewall/WAF appliances, Linux/Windows servers, databases, and enterprise applications using Syslog, Fluentbit, Logstash, and secure REST APIs.
What is the expected timeline for deploying SIEMz?
Using automated Infrastructure-as-Code (IaC), core SIEMz platform components deploy in under 30 minutes. Following core deployment, our local advisory engineers assist with log source onboarding and custom security dashboard configuration.
How To Connect With Us
Choose the communication channel that best suits your cybersecurity team:
Official WhatsApp
+60 16-615 7156
Connect directly with our cybersecurity consultants via WhatsApp.
Open WhatsApp →hello@siemz.my
rahman@amancloud.com
For official RFPs, enterprise tenders, or formal quotation requests.
Send Email →Kuala Lumpur, Malaysia
Monday – Friday: 9:00 AM – 6:00 PM (GMT+8)
Critical Incident Response: 24/7/365
Request a Technical Demo & Official Quotation
Please fill in your details below. Our cybersecurity solutions engineering team will connect with you within 24 hours.